Hyron AI
Finds the risky packages in a project's npm dependencies, explains each score, and plans safe upgrades. FUSION 2026 hackathon — team lead.
- AI model
- Deterministic rule
- A person reviews
- Not working yet
- inputnpm lockfiles
- serviceDependency graph
- ruleOSV + EPSS + CISA KEV
- ruleExplainable risk score
- personUpgrade plan: auto / review / block
- 24-hour hackathon build
- OSV + EPSS + CISA KEV
- Explainable 0–100 score
- Team of four
The problem
A project's real risk sits deep in its transitive npm dependencies, and vulnerability lists don't say which findings matter most or what upgrading would break.
Approach
Led a four-person team that built, in 24 hours, a scanner that maps direct and transitive dependencies across projects and ranks findings with a transparent score instead of a raw list.
Architecture
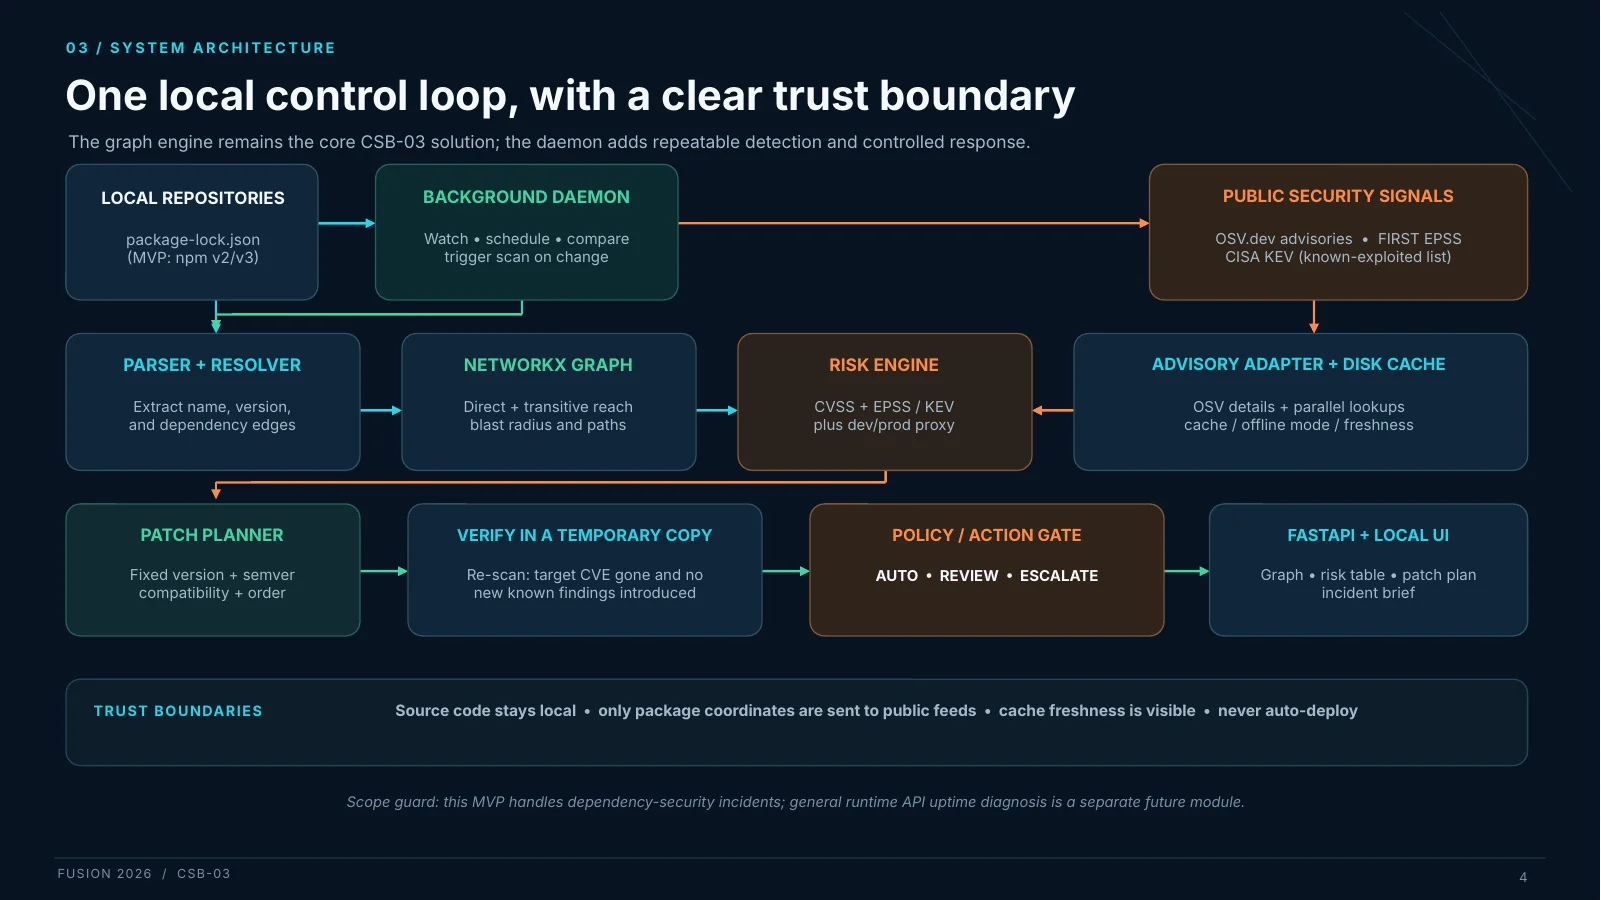
Reads npm lockfiles and builds a dependency graph in NetworkX (npm's nearest-node_modules resolution). Each package is checked against OSV.dev advisories and scored with CVSS, FIRST EPSS and CISA KEV into an explainable 0–100 risk score, with blast radius across projects. Upgrade plans stay within semver and pass an AUTO / REVIEW / BLOCK gate. FastAPI backend, React dashboard.
Results and limits
Working scan → score → upgrade plan on real npm projects. Limitations: reachability is not analysed, and verification re-scans advisories rather than installing and testing the upgrade. Next: a GitHub Action version and pnpm / yarn / Python lockfiles.